The CISO (Chief Information Security Officer) or ISO (Information Security Officer) plays a crucial role in ensuring information security in companies and organizations.
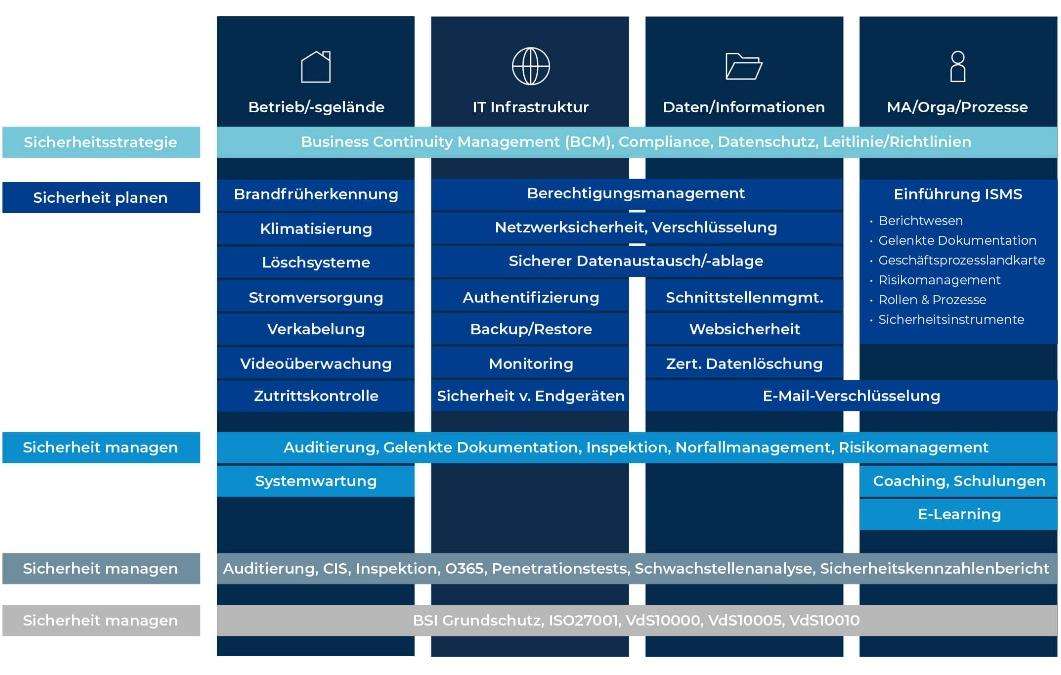
We see information security as a management system that is planned and regularly adapted to the current situation. It is based on an inventory and risk assessment that starts from your company's value-creating processes.
The following areas are addressed:
Another goal is to ensure compliance with relevant security standards and regulations, to strengthen the trust of customers and business partners in how their data is handled, and to relieve executive management of liability. To this end, we offer you the right service package for your needs as ongoing support.
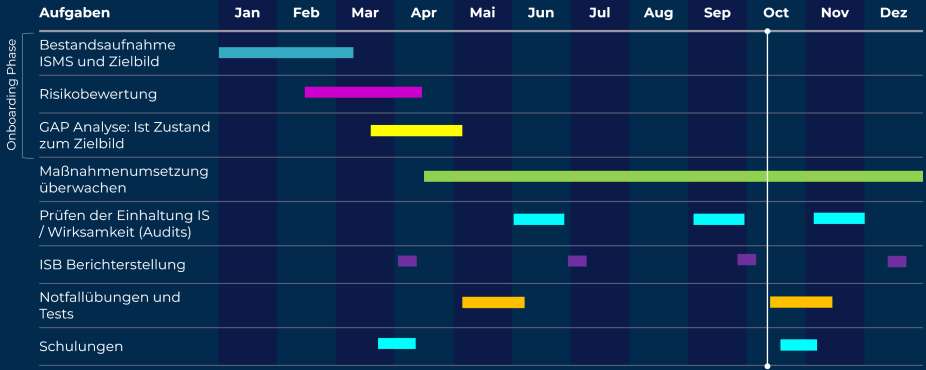
How do we proceed? (Example)
DURATION AND SCOPE OF THE ENGAGEMENT
Initial workshop at a
fixed price, then 12 months
ONBOARDING PHASE
Getting up to speed with the existing ISMS
Introduction to relevant contacts
Align on tooling
Close priority 1 gaps
ONGOING SUPPORT
Monthly flat fee and coordination of special topics Ticket system and GRC
tool for easy maintenance of the ISMS
We hold an initial workshop to align on tasks, define the scope and schedule the activities, and we provide you with the results.
On this basis, we specify the scope, tasks and effort for providing your ISO. If necessary, this is reviewed and adjusted monthly to account for special tasks.